Hi All,
I'm currently trying to setup RAS 19.2.3 using SAML authentication in a test lab but it seems after a successful logon on our IDP the RAS server is not able to match the NameID attribute that is properly recognized from the SAML assertion with the userPrincipalName AD User attribute. I have manually checked the AD attribute for the user and can even run a Get-ADUser command and filter for the UPN in the SAML assertion and it returns the proper user account in AD. But somehow RAS cannot match the user account. Is there any possibility to enable some enhanced logging from RAS to see how it tries to find the user in AD or does anyone have some inputs what I might be doing wrong?
RAS Controller Log entries:
[I 06/00000038/T1784/P0740] 21-08-23 18:39:27 - Agent vmsparalells01.XXXXXXXXXXX.com (Secure Gateway) was enabled. Code AgentState::OK
[I 06/0000000E/T0CC4/P0740] 21-08-23 18:39:55 - User (f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com) connected from client (192.168.2.195:50625), machine (html5-a84246ab)(FF-FF-A8-42-46-AB) mode Gateway SSL, using OS: HTML5, Client version: 19.2.3 (build 24005).
[E 72/00000006/T0CC4/P0740] 21-08-23 18:39:55 - SAML - User:'f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com' - Failed to find AD user for f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com
[E 0E/0000002C/T0CC4/P0740] 21-08-23 18:39:55 - SAML: Failed to Identify User from Assertion
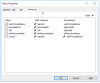
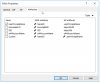
SAML Attribute config:
Decoded Assertion:
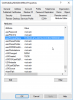
AD Account Attributes:
Get-ADUser output:
I'm currently trying to setup RAS 19.2.3 using SAML authentication in a test lab but it seems after a successful logon on our IDP the RAS server is not able to match the NameID attribute that is properly recognized from the SAML assertion with the userPrincipalName AD User attribute. I have manually checked the AD attribute for the user and can even run a Get-ADUser command and filter for the UPN in the SAML assertion and it returns the proper user account in AD. But somehow RAS cannot match the user account. Is there any possibility to enable some enhanced logging from RAS to see how it tries to find the user in AD or does anyone have some inputs what I might be doing wrong?
RAS Controller Log entries:
[I 06/00000038/T1784/P0740] 21-08-23 18:39:27 - Agent vmsparalells01.XXXXXXXXXXX.com (Secure Gateway) was enabled. Code AgentState::OK
[I 06/0000000E/T0CC4/P0740] 21-08-23 18:39:55 - User (f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com) connected from client (192.168.2.195:50625), machine (html5-a84246ab)(FF-FF-A8-42-46-AB) mode Gateway SSL, using OS: HTML5, Client version: 19.2.3 (build 24005).
[E 72/00000006/T0CC4/P0740] 21-08-23 18:39:55 - SAML - User:'f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com' - Failed to find AD user for f1c54cb4-af1a-4b4f-bc04-fc6fdc988660@XXXXXXXXXXX.com
[E 0E/0000002C/T0CC4/P0740] 21-08-23 18:39:55 - SAML: Failed to Identify User from Assertion
SAML Attribute config:
Decoded Assertion:
AD Account Attributes:
Get-ADUser output: