Cannot enable TPM, TPM option missing from add hardware menu

KarstenS6

Bit poster
I tried to enable TPM by following the instructions to enable the Trusted Platform Module. The instructions do not work, because there is no "TPM chip" option on the add hardware menu. I see only Network, Printer, Hard Disk, CD/DVD, and Serial Port.

I am using Parallels Desktop for Mac Pro Edition v15, build 46967. The overview states that it should work in the Pro and Business editions.

Is there some other step missing from the instructions?

Thanks,
-- K
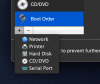
Screen Shot 2019-08-15 at 03.09.52.png

Screen Shot 2019-08-15 at 03.10.51.png
 
Platform Trust Technology (PTT) is enabled on these systems by default, causing the TPM to be greyed out in the BIOS (Only one of these trust technologies can be enabled at a time). To enable TPM, PTT protection must be removed from the encryption keys.
To disable the PTT Protection and encrypt the hard drive through TPM:
  1. Suspend BitLocker if it has been initiated.

  2. Restart the system, and enter the BIOS

  3. Disable Secure Boot in the BIOS.

  4. Under Security Settings: Disable PTT, Enable TPM, Activate TPM, then save the changes

  5. Restart to the operating system and enable BitLocker
BitLocker should be functioning on the TPM once this is complete.
This configuration is currently seen in the Dell Latitude 10/ST2 and Venue 11 designs. Future systems may also include this technology.
 
my OS is windows 10
I am trying to upgrade to windows 11 without install another VM
id 380505147

I see after you set <EfiEnabled> to 1, and VM still booted into Windows.
Then you powered off it properly.
Then you have added TPM into config. And only after this step VM didn't boot.

I guess you didn't run 'mbr2gpt' in Windows. It should be the first step.
See excellent post for guidance.
 
I'm using the trial version of parallels 17.1.0 and I have no TPM option. bios is EFI. Am I missing something here?
BRIANM32, what type of guest OS is set on "General" tab of VM configuration editor. It should be set to Windows 10 or Windows 11.
Also, TPM in not available for Bootcamp based VMs. How did you set bios type to EFI? If you set it via boot flags of Advanced windows it won't work.
 
Back
Top